An agent’s true cost isn’t only the tokens it burns. It’s the review that calls your code “safe to merge” after seeing the diff, but without any context on the pipeline. We call that artificial confidence, not artificial intelligence. Agents guess because code is all they can see; they can’t see the merge request that last changed it, the pipeline that ran it, the vulnerability it carries, or the people who wrote and reviewed it.
Guessing is expensive. If you’ve tried running agents in a large monorepo, one with tens of thousands of files, you know how it goes: the agent iterates, pinging the backend again and again for the information it needs to complete the task. Every round trip costs more time and more tokens. Eventually the agent gives up.
The model isn’t the constraint. Context is.
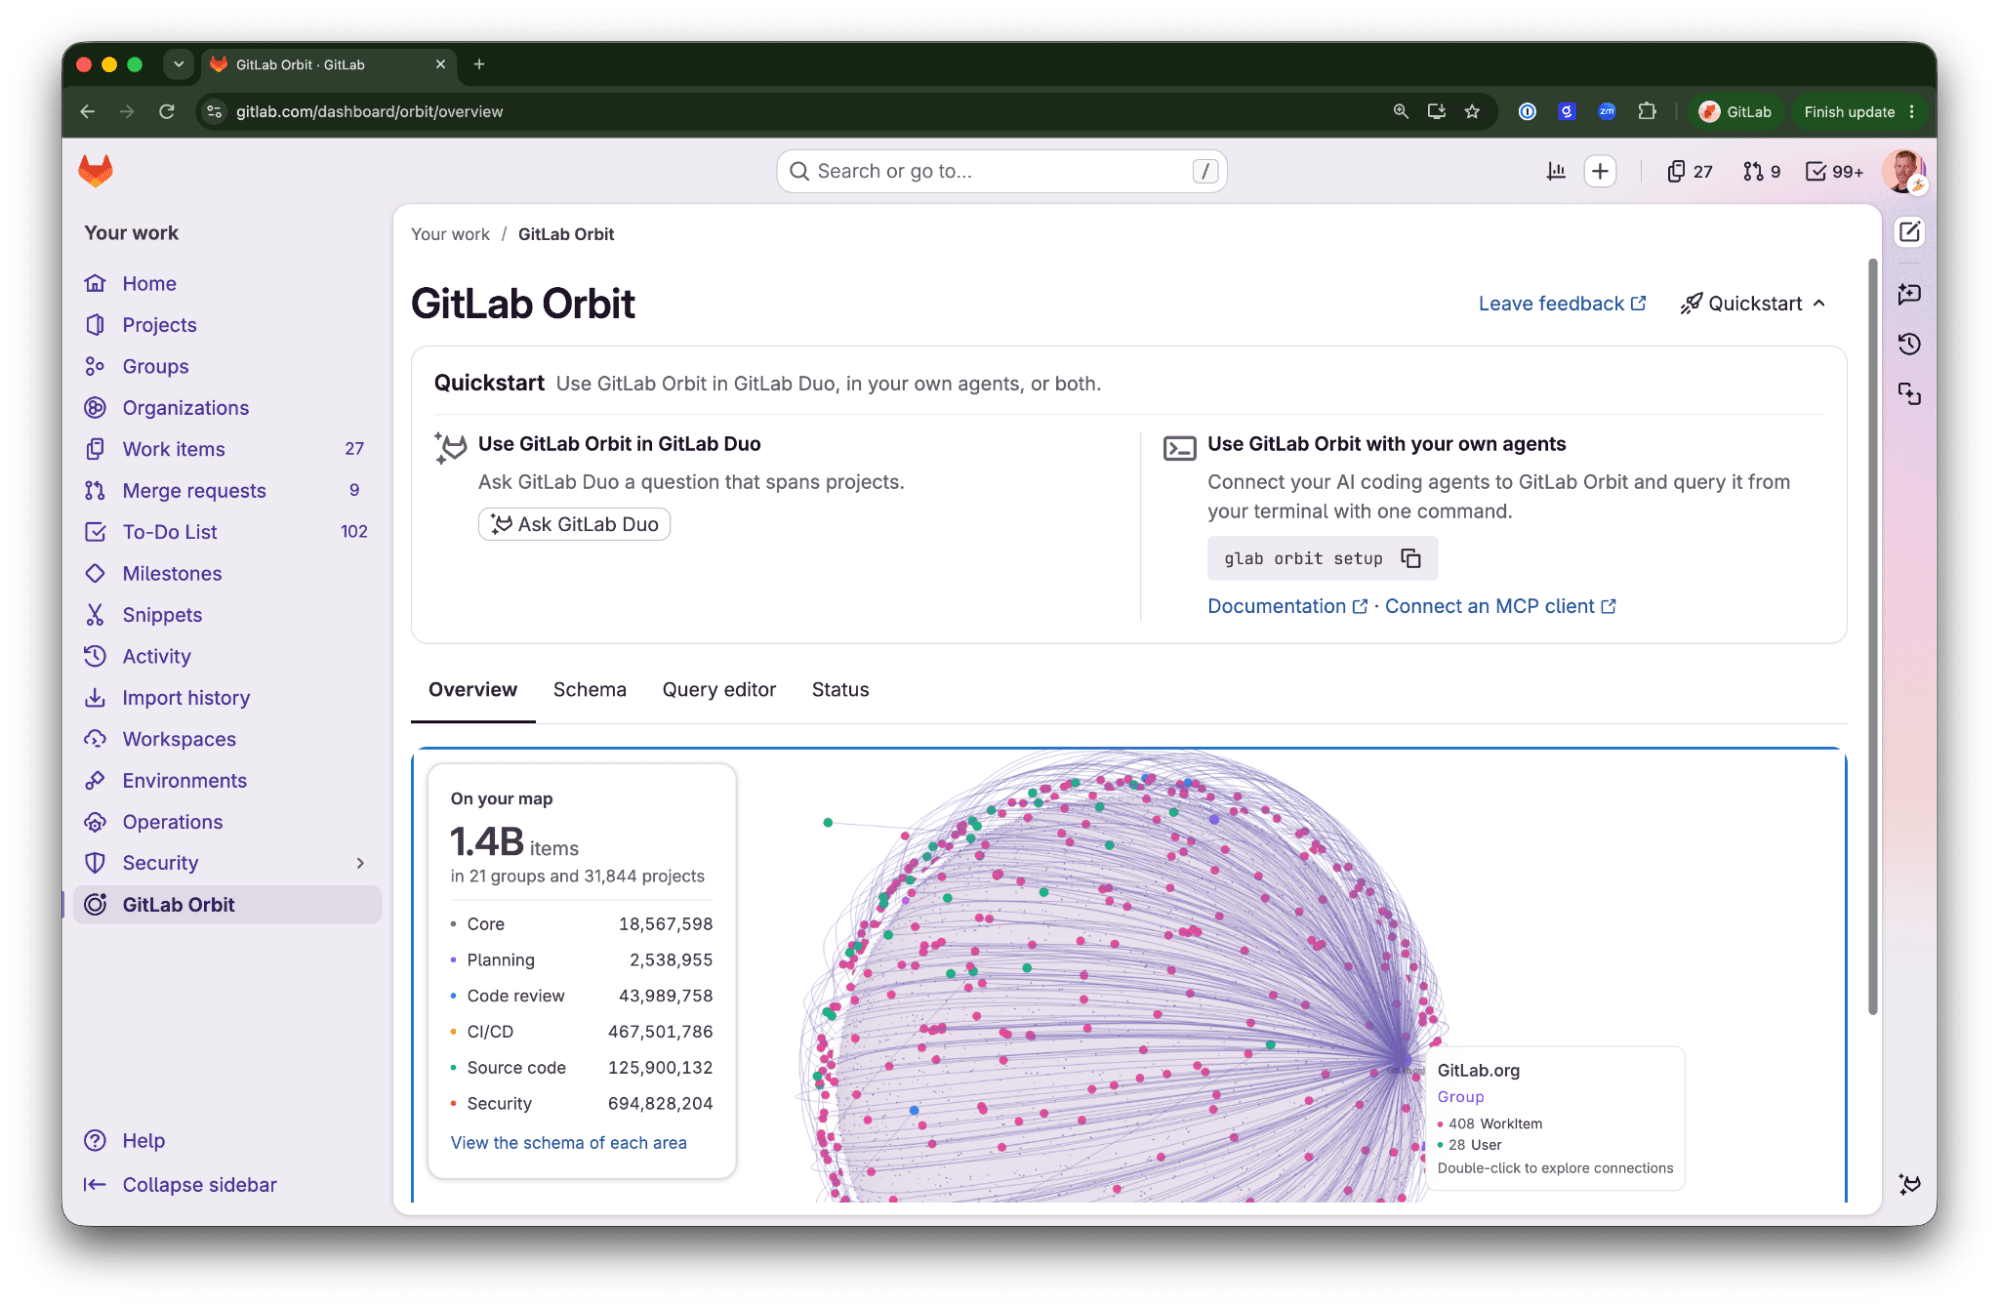
That’s the constraint that GitLab Orbit removes. Now generally available, Orbit is the context graph for your software lifecycle: a live, queryable view of all your code, merge requests, work items, pipelines, vulnerabilities, and ownership, with every relationship continuously updated as you ship. Every agent and engineer can work from one connected view of the lifecycle. In GitLab testing, agents connected to Orbit needed up to 45x fewer retries and used 4.5x fewer tokens on the same tasks with the same model.
Grounded agents get answers right the first timeAn agent like Claude Code, connected to GitLab Orbit through MCP, stops crawling files and instead asks the graph. The first response comes back with real callers, recent changes, and owners, so your follow-up prompts can refine the answer rather than correct it. The difference is measurable. Compare the Market, one of the UK’s largest price comparison platforms, tested four context approaches for an internal AI code reviewer across 79 real merge requests. The GitLab Orbit-grounded reviewer matched about 70% of expected inline comments; RAG managed about 58%, worse than no added context at all.
Fewer retries means fewer tokens“GitLab Orbit gave us an AI code reviewer that actually understands our codebase, not just the diff in front of it. We tested it against RAG and a few other approaches across real merge requests, and the gap was clear. Better comment placement, better summaries of what actually changed.”
— Ryan Harvey, Head of AI Engineering, Compare the Market
A recent analysis from a leading research and advisory firm found that the cost of an undisciplined agent session is dominated by retransmitting context that didn’t change between turns. That token cost comes from how the agent is set up, not from the model itself.
GitLab Orbit changes that engineering. The agent gets one bounded answer from the graph instead of reloading everything that might matter. In GitLab testing, agents connected to Orbit used up to 4.5x fewer tokens on the same tasks with the same model: each turn carries less context, and fewer turns go to work that never ships. Because the graph is shared, that cost doesn’t repeat per agent. Duo agents, Claude Code, Codex, and your own tools all query the same graph, so the context you build for the first agent is already there for the second.
Questions you couldn’t answer beforeSince GitLab Orbit entered beta in June, we’ve worked with design partners running it against real codebases, real incidents, and real merge requests. Their first win was almost always a question they couldn’t get answered before.
Here are a few questions design partners asked Orbit that they couldn’t answer before, and what came back:
Which production services are exposed to this vulnerability? A single query returns the services that include the component, the merge requests that introduced it, the environments it reached, and the teams that own each one. One design partner answered a security-coverage question across 34 million entities in seven minutes; through the API, the same question would have taken half a day. When a vulnerability lands, security has a complete remediation plan within the hour, not a partial list by the end of the day.
What breaks if I change this? Before a push, a developer or their agent can ask which services, jobs, and environments a change touches, across every project in the group, not just the one open in the editor. Review agents bring the same answer to the merge request, so a “safe to merge” comment reflects the whole system instead of the diff. Across 79 real merge requests, Compare the Market’s reviewer flagged more real issues in the right places than their RAG-based version. Problems get caught in review, before they become outages.
Why does this CI job keep failing, and where else? GitLab Orbit shows how often a job fails across every project that runs it, which projects have drifted from the shared CI configuration, and who owns them. What used to be a Slack thread asking three teams “has anyone seen this?” becomes one answer. A financial services company used this to trace a build-system outage to a CI job failing 50% of the time, a pattern nothing else had correlated.
What depends on the thing we’re about to migrate? Every dependent service, job, environment, and owner comes back in one result. One design partner finished a multi-repository upgrade by asking the question directly: which projects are still on the old version? The last stragglers could be surfaced in one query with no spreadsheet or repo-by-repo audit to contend with.
Not every context graph can answer themContext graphs are becoming a category, and most of them stop at code. GitLab connects the code change to the pipeline, the deployment, the vulnerability, and the owner, with your permissions intact. This means your team and agents can:
- Start with a graph that already exists. GitLab Orbit draws on the data you already have in GitLab, which means there is no connector to configure, no ETL pipeline to maintain, and no second system of record to keep in sync. Enable it for a group and the graph is ready. A graph assembled from the outside takes months of integration work before it answers its first question. Orbit is also built to extend to non-GitLab data sources.
- Index the whole lifecycle. GitLab is the system of record for the entire software development lifecycle, and GitLab Orbit connects it into one graph. Code indexes stop at the code. Work graphs stop at the ticket.
- Keep your permissions without rebuilding them. GitLab Orbit mirrors nested groups, roles, and security-domain access. A graph that lives outside GitLab has to rebuild all of that and keep it in sync.
- Give every agent and every engineer the same graph. Duo agents, Claude Code, Codex, custom tools, and the Data Explorer all query the same graph the same way. You invest in context once and every agent you add after that is cheaper than the last.
GitLab Orbit doesn’t ask you to change how your team works. The agents and tools you already run connect to one graph:
- Agents on GitLab Duo Agent Platform query GitLab Orbit natively, with nothing to configure.
- Claude Code, Codex, Cursor, OpenCode, Gemini CLI, Antigravity, and any other MCP-compatible agent connect through MCP or the GitLab CLI:
glab auth login
glab orbit setup
- Custom agents and internal tooling connect through REST.
- Engineers query the same graph through the Data Explorer.
Every path asks the same graph the same way, and the graph keeps up. GitLab Orbit indexes every push, merge, and deploy as it happens, so agents reason from the lifecycle in its most current state; at GitLab’s scale, that’s more than 1.5 million projects and 8TB of graph data in under 2 hours. Indexing runs as its own service beside GitLab, so however hard your agents use Orbit, GitLab itself never slows down.
Pricing: One shared query pool for your whole organizationGitLab Orbit is sold as query packs that form one shared pool sized for your organization. Everyone in your GitLab org draws from it, humans and agents alike, so usage flows between occasional users, power users, and the agents working on their behalf. Nobody requests access or gets assigned a seat. A query is one request to the Orbit graph, whether it comes from an agent (such as Duo Agent Platform, Claude Code, or Cursor), an experience built into GitLab, or the API.
Each query pack is $30 in GitLab Credits per user per month and adds 1,000 queries to your organization’s shared pool; usage beyond the pool is billed at 33 queries per GitLab Credit, about $0.03 per query. Promotional pricing is available this quarter for early customers. Contact your GitLab account team to learn more and size the right number of query packs for your organization.
Get started with GitLab OrbitGitLab Orbit is now generally available for Premium and Ultimate customers, starting with GitLab.com today and reaching Self-Managed and GitLab Dedicated over the coming weeks. Customers can try it free for 30 days through their GitLab account team. If you’re brand new to GitLab, talk to our sales team about getting started with a GitLab paid plan, and we can help you add an Orbit trial as part of it.
Check out our documentation to help you get started.
Thank you to our design partners and beta participants, whose candid feedback from real codebases helped to shape today’s GA release.
This blog post contains "forward‑looking statements" within the meaning of Section 27A of the Securities Act of 1933, as amended, and Section 21E of the Securities Exchange Act of 1934. Although we believe that the expectations reflected in these statements are reasonable, they are subject to known and unknown risks, uncertainties, assumptions and other factors that may cause actual results or outcomes to differ materially. Further information on these risks and other factors is included under the caption "Risk Factors" in our filings with the SEC. We do not undertake any obligation to update or revise these statements after the date of this blog post, except as required by law.